 LIVE DEMO
Fix Proof
Tradespeople log each repair with photos and a customer signature, sealed onchain as a warranty.
Yours in 1 to 2 days
$100Base · Polygon +1
 Try it live
A pre-audit kit for small teams: open source checks on your repo, every finding explained in one plain sentence, a fix tracker and an audit-ready folder for auditors and audit subsidy programs.
Try it live, freeYour USDC is locked in a smart contract, not sent to us. The contract lets us collect it only if we deliver within 14 days of your payment (by 16 Nov 2026 if you pay today). After that date, if we have not collected it, you take it back yourself from My apps, no permission needed. Before it, only we can refund: if we miss the promised date, ask in My apps and we refund you from the contract. View the contract on BaseScan. This covers every payment, a reservation too: the funds are released to us only when we deliver.
Promised delivery: 8 Nov 2026 (counted from payment). Self-refund opens: 16 Nov 2026 (the contract deadline).
Add-ons are not part of this payment. Once your app is delivered you can request them from My apps, and you only pay if you say yes to the quote.
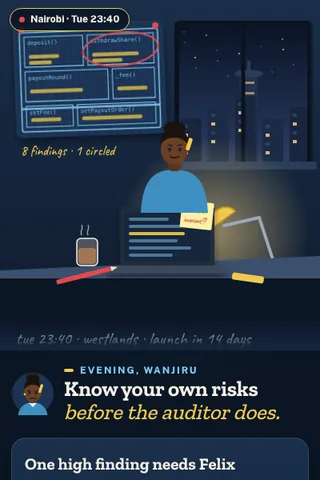
Wanjiru Kamau is the product half of a two person team in Nairobi building Chama Vault, a group savings contract for Arbitrum and BNB Chain. Two weeks before launch an auditor quoted six weeks and asked for the invariants, and she did not know what the word meant. Audit Ready ran open source static checks on the repo, explained each of the eight findings in a sentence she could repeat to her members, tracked what her co-founder Felix fixed, and packed scope, invariants, coverage and a deployment plan into one folder she could send to an auditor and attach to an Arbitrum Audit Program application. It never told her the code was safe.
One hosted Audit Ready app: connect a GitHub repo with Foundry or Hardhat, run Slither and Aderyn plus forge coverage in a sandbox, plain-words explanation for every finding, fix tracker with fixed, explained or accepted states, threat model and invariants editor with prompts, known unknowns page, deployment plan for BNB Chain, Arbitrum, Avalanche, Linea and Ethereum, an exportable audit-ready folder and a share link for auditors.
Reshape it entirely: new features, your flows, your brand end to end, integrations you need. We scope it with you.
Static analyzers (Slither, Aderyn, Mythril) and coverage tools are mature and free, and audit firms publish readiness checklists. What is new is the bundle and the voice: every raw finding gets a one sentence explanation a non auditor can repeat, the team marks each one fixed, explained or accepted with a reason, a known unknowns page lists what tools cannot check, and the result is one audit-ready folder shaped for auditors and audit subsidy programs.
Slither and Aderyn for static analysis, Foundry coverage, Code4rena and Sherlock readiness guides, and paid scanners such as Olympix and SolidityScan. All live; none pairs plain explanations with a packaged audit-ready folder for subsidy programs.
Checked with web searches in October 2026. A search is not proof that nothing similar exists, and the market moves fast, so we recheck before every build.
14 live races fit this app. Each one says why, with its prize and countdown. The rule on existing code is on the race page.
A complete pre-audit app you own: small teams connect a repo, read every finding in one plain sentence, track fixes and export an audit-ready folder, and pay you monthly for rescans, the folder and multi repo plans. Your console runs pricing, growth, rules and the scan agent.
Every buyer gets the same finished app. Basic branding and copy changes come through a quick form.
Your admin side: revenue, paywall editor, users, rules and the agent log.
Referral and growth mechanics, switched on when you are ready to grow.
A free plan for one repo and a weekly scan, and monthly plans for unlimited rescans, the fix tracker, folder export and multiple repos. You never sell audits or approvals.
Prices are yours to set. Illustrative, not a promise of income.
Unlocked when your app is paid in full
Unlocked when your app is paid in full
Your brand, a version for one audit firm or accelerator, extra tools, other languages such as Rust for Solana or Move, or a white label intake for a grant program are scoped and priced together.
The recipe (how it is built, the data, costs, risks, build order, the pitch and the demo script) is unlocked when your app is paid in full.
Small teams get to launch week with contracts nobody outside the team has read. Auditors ask for scope, invariants, coverage and a deployment plan, and audit subsidy programs ask for much the same, but non technical founders often cannot tell a real risk from tool noise. They either pay to have an auditor sort basic findings or skip review entirely.
The tools exist and are free: Slither and Aderyn find common Solidity issues, Foundry and Hardhat report coverage, and audit firms publish readiness checklists. Audit Ready is an incremental take that bundles them for founders: one sentence explanations for every finding, a fix tracker with fixed, explained or accepted states and a written reason, a threat model and invariants editor with prompts, a known unknowns page, and one exportable folder for auditors and audit subsidy programs. It does not replace an audit and never says code is safe. Research verdict: exists in parts, medium novelty in the bundle.
Unlocked when your app is paid in full
Every small team should walk into an audit understanding its own risks, in plain words, with nothing hidden and nothing claimed that the tools cannot know.
One sentence per finding Each raw tool finding comes with a plain sentence, such as: someone could pull their share twice before the balance updates. The founder can repeat it to members.
Fixed, explained or accepted Nothing is silently dismissed. Every finding ends in one of three states with a written reason, which is what auditors want to read first.
Known unknowns A page that lists what static tools cannot check: business logic, economic attacks, admin key handling and anything offchain. It is the most honest page in the folder.
The folder Scope, invariants, coverage, deployment plan, threat model and responses, exported as one folder with a share link and an optional onchain hash.
Unlocked when your app is paid in full
Cost per use: unlocked when your app is paid in full.
The share link to an auditor carries a small Prepared with Audit Ready line, and accelerators, hackathons and audit subsidy programs can hand teams an intake link. A monthly anonymous report of the most common findings brings founders back.
Unlocked when your app is paid in full
Unlocked when your app is paid in full
Costs and tools are estimates at the time of writing. General information only, not legal or financial advice.
Nine routes from one vessel. Tap a port to open its chart.
Thousands of small teams ship contracts every month, and most of them reach launch week without anyone outside the team reading the code. Owning Audit Ready means you run the honest pre-audit desk: open source checks, every finding in a sentence a founder can repeat, a fix tracker and one folder an auditor can start from. You earn from monthly plans, never by selling approvals or calling code safe.
Yes, because the app is not an audit and says so on every screen. It runs well known open source tools, explains their output with reviewed templates and packages the team's own answers. You run the app and support teams; auditors still do the audits.
That can happen, and the app never claims otherwise. It shows no safety score, keeps a known unknowns page in every folder and tells teams to get a professional audit. Keep that wording, and never market the app as a security guarantee.
Access is read only to one repo, scans run in an isolated sandbox and code is deleted from workers after each run. Publish that plainly, and offer a local run option for teams that want it.
The tools are free; turning their output into plain words, a fix history and a folder auditors and programs accept is the work people pay for. Teams that save even one day of an auditor's time come out ahead.
Monthly plans for rescans, the fix tracker and folder export, a Studio plan for accelerators and auditors, and white label intake for programs. Illustrations, not promises.
Illustrative stages, not a forecast. Results depend on you and the market; nothing here is guaranteed.
LIVE DEMOTradespeople log each repair with photos and a customer signature, sealed onchain as a warranty.
 LIVE DEMO
Leave clear onchain instructions so the people you trust can reach your crypto if you cannot.
 LIVE DEMO
A weekly ritual that finds risky token approvals and lets you revoke them in one tidy pass.
 LIVE DEMO
Every commit, deploy, and demo you ship becomes a signed, timestamped builder diary.
 LIVE DEMO
Show funders exactly what their grant built, milestone by milestone, with proof attached.
 LIVE DEMO
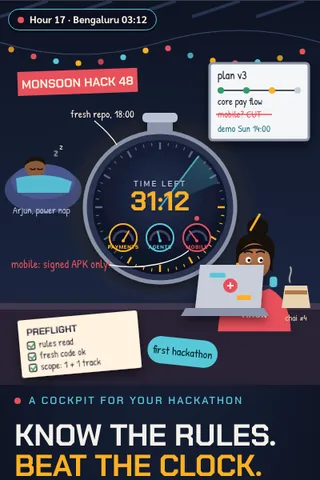
A hackathon cockpit that plans your scope, tracks bounties, and drafts a judge-ready submission.
 LIVE DEMO
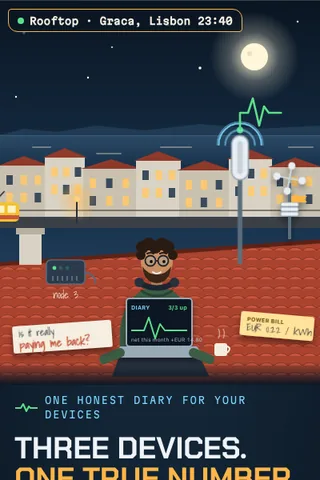
Your DePIN devices report uptime and earnings in one honest dashboard with tax-ready exports.
 LIVE DEMO
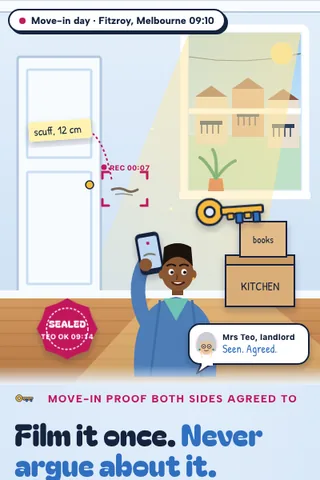
Tenants and landlords seal move-in photos and rent receipts so deposit disputes end fast.